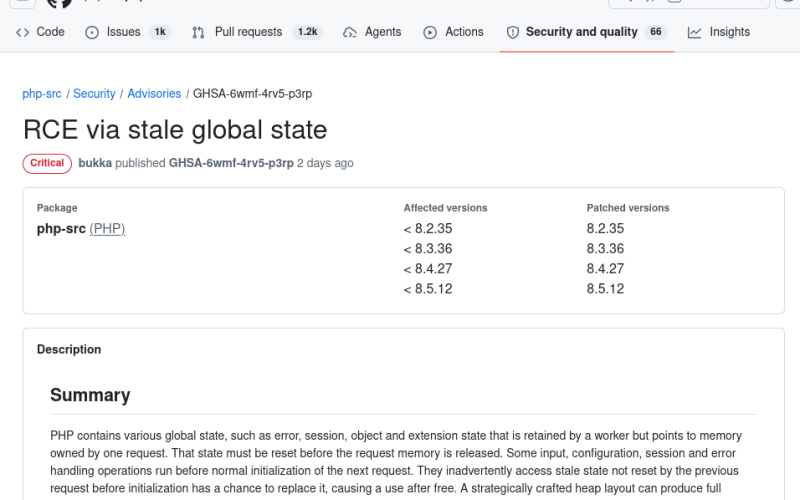
A pair of critical Remote Code Execution (RCE) vulnerabilities—collectively tracked as PHP2Shell—has been uncovered in PHP. Rated 9.2 out of 10 on the CVSS scale, these flaws affect unpatched PHP installations globally and allow unauthenticated attackers to run arbitrary code on web servers.
Key Details:
The Flaws: Discovered via AI-assisted code auditing, the vulnerabilities stem from memory corruption during out-of-memory (OOM) handling (CVE-2026-109618) and stale global state management (CVE-2026-109619).
Impact: Every PHP setup serving web requests (including PHP-FPM, Apache mod_php, and CGI variants) is potentially at risk, with attacks possible before application code even executes.
The Fix: The PHP development team has released emergency patches. Administrators must update immediately to PHP versions 8.5.12, 8.4.27, 8.3.36, or 8.2.35 (and restart all workers). Unsupported versions (PHP 8.1 and older) require upgrading or manual backports, as they will not receive official updates.